
 Thought Leadership
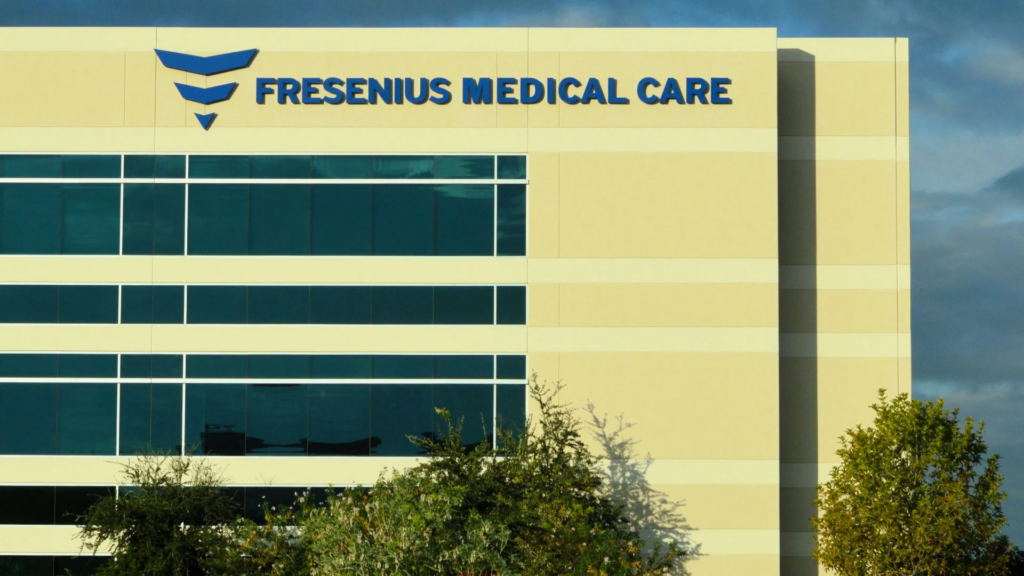
Fresenius Medical Care has reported a cybersecurity incident after attackers gained access to internal systems.
Fresenius Medical Care (FME) has been targeted in a cyberattack. In a media statement, the dialysis company, based in Bad Homburg, Germany, confirmed that there had been “unauthorized access to a limited number of internal systems.” The incident is currently under investigation. The impact appears to be limited. According to FME, the incident had “no impact on medical devices, patient care, production, or ongoing business operations.” For a company whose dialysis equipment and clinics are critical to patients with kidney failure around the world, that is arguably the most important piece of information.
External Experts and Authorities Involved
“As soon as the incident was detected, FME immediately took steps to contain and remediate the situation,” the company said in its statement. FME has also brought in leading cybersecurity experts and notified the relevant law enforcement authorities. As part of the investigation, the company said it is complying with all applicable legal and regulatory requirements.
Many Questions Remain Unanswered
Beyond that, the statement provides little detail. FME has not disclosed when the attack took place or when it was detected. It has also not said what type of attack was involved, such as ransomware, or which specific systems were affected. One key question also remains unanswered: whether any data was exfiltrated and whether it included personal information belonging to patients or employees. Instead, the company reiterated the standard commitment that “protecting the security of our systems and the privacy of those who rely on us remains our highest priority.”
Healthcare Sector in the Crosshairs
The healthcare sector has been a preferred target for cybercriminals for years. One high-profile example this year was the attack on medical technology manufacturer Stryker. Hospitals, pharmaceutical companies, and medical device manufacturers hold sensitive data and face enormous pressure when operations are disrupted, making them attractive targets for extortion attempts.
Whether a ransomware group will claim responsibility for the attack on FME may become clear in the coming days.
(Editorial Team)