
 Thought Leadership
Temperature and defrost settings were manipulated at three facilities. According to EFS, no blood products were lost. Refrigeration provider Coolworld points to a third-party component.
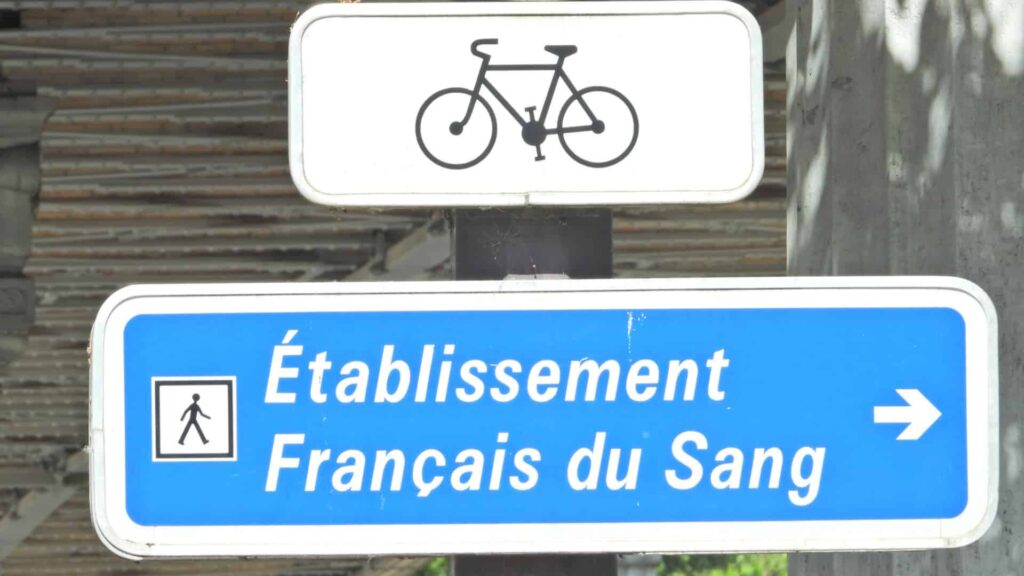
France’s national blood service, Établissement français du sang (EFS), has confirmed that a cyberattack on November 2 disrupted refrigeration systems at three of its facilities. The attack did not directly target EFS but rather a refrigeration service provider. The affected systems were used to monitor and control cold storage rooms where blood products are stored before delivery to hospitals, along with biological samples. The attackers changed the temperature limits and defrost settings to extremely high values. Earlier, the French weekly newspaper Le Canard enchaîné reported that cold storage rooms normally operating at minus 30 degrees Celsius had been configured to reach 110 degrees Celsius.
No Blood Products Lost
According to EFS, its monitoring and alarm systems quickly detected the temperature changes. Staff were able to repair the affected equipment or transfer the products to other cold storage rooms. Plasma bags intended for transfusions and plasma used in pharmaceutical manufacturing were relocated or secured.
“No health impacts have been identified, and no loss of blood products has been reported.”
EFS
Blood donations and supplies have continued without interruption. EFS is working with France’s national cybersecurity agency, ANSSI, and the Ministry of Health. It has also increased monitoring of its refrigeration systems.
Service Provider Points to Third-Party Component
EFS did not identify the affected service provider. However, European refrigeration company Coolworld Rentals confirmed a security incident involving its remote monitoring software, which affected a limited number of its refrigeration units. According to Coolworld, the attackers exploited a vulnerability in a third-party component that was outside the company’s direct control. The company did not disclose which component was involved.
Wave of Attacks Across Several Countries
The incident is part of a series of attacks targeting refrigeration systems across Europe. In October, attackers disrupted refrigeration systems at an estimated 250 to 350 French supermarkets by triggering automatic defrost cycles through controllers running older Danfoss software. According to BleepingComputer, the affected devices included Danfoss AK-SM and AK-SC controllers, as well as Copeland/Dixell XWEB systems.
A second wave of attacks in November affected more than 115 stores in Belgium, the Netherlands, Sweden, Luxembourg, Ireland, and Estonia. According to Belgian refrigeration company Sabcobel, the attackers exploited the same vulnerability used in the October incidents.
In 2025, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) disclosed two vulnerabilities affecting Danfoss AK-SM 8xxA controllers. These flaws allow attackers to bypass authentication and execute commands remotely. However, it has not been confirmed whether the vulnerabilities were exploited in these attacks.
Germany’s Federal Office for Information Security (BSI) recommends that operators ensure control systems are not directly accessible from the internet. Remote access should only be permitted through VPN connections with multi-factor authentication (MFA). This recommendation also applies to external service providers responsible for maintaining the equipment.
(Editorial Team)