
 Thought Leadership
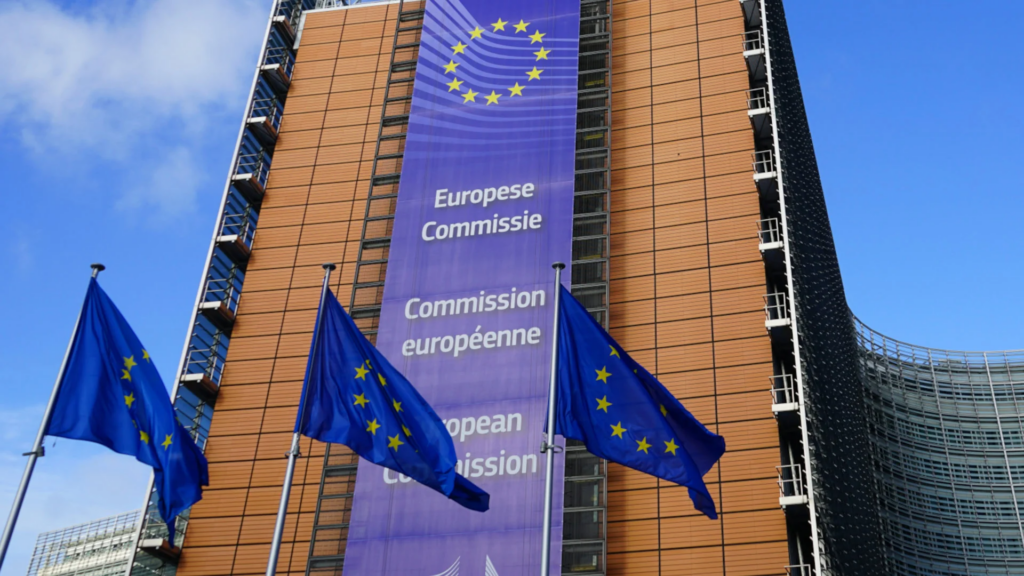
The European Commission has reported a cyberattack that may have exposed employee data. The attackers reportedly used Artex, an open-source framework that enables AI agents to autonomously attack networks and has increasingly been abused since the summer.
The European Commission has fallen victim to a cyberattack. Politico’s Playbook newsletter reported the incident, citing an EU official. Large amounts of personal data may have been exfiltrated. The Commission’s leadership discussed the incident at its weekly meeting on Wednesday. The attack also had direct consequences for employees: salary and vacation information could temporarily no longer be entered into internal systems. Several applications were taken offline as a precaution. Most have since been restored.
“The Commission believes it has contained most of the attack, but the full extent of any damage remains unclear. The systems may be coming back online. The answers are taking a little longer.”
Anonymous EU official
According to the official, the Commission believes it has contained most of the attack. However, the full extent of the damage remains unknown. Commission spokesperson Thomas Regnier confirmed that the institution had responded to an identified cyber campaign. Individual systems were targeted, and those affected have been notified. Investigators are currently examining whether employee data was compromised.
CERT-EU Detects Artex in Use
The tool used in the attack is particularly noteworthy. In early November, CERT-EU, the cybersecurity incident response team for EU institutions, observed international threat actors deploying Artex. The publicly available tool uses AI to identify vulnerabilities in IT systems. According to the EU official, some threat actors are abusing tools of this kind and used them to target the Commission.
Artex is an open-source, multi-agent penetration testing framework controlled by large language models (LLMs) and written in Go. A developer from China using the handle Autumn-27 published it on GitHub in July 2026, reportedly for educational purposes and to test systems they owned or were authorized to assess. Like Cobalt Strike and Metasploit, Artex is therefore a dual-use tool. It is not classified as malware and consequently has no CVE identifier.
One Operator, Multiple AI Agents
Artex works fundamentally differently from traditional vulnerability scanners. A single operator defines the target, while a team of AI agents handles the rest of the attack chain. Planning agents map the targets and determine the next steps. Execution agents scan systems, exploit vulnerabilities, deploy web shells and collect credentials. Their findings are fed back to the planning agents, which then initiate the next wave of attacks. Google and Mandiant describe six sub-agents and have observed 27 events within just 23 seconds.
External tools such as Nmap, Nuclei and browser automation are integrated as interchangeable MCP servers, which the agents can discover themselves at runtime. The framework is also model-agnostic and works with any LLM API. Real-world attacks have involved DeepSeek v4.1-flash, GLM-5.3 from Zhipu AI and Grok 4.6. A single intrusion consumed approximately 1.4 billion input tokens.
According to security researchers, Artex does not introduce a new type of attack. However, it makes established attack techniques faster and cheaper. Qualys notes that the tool does not change what attackers exploit, but it does change how much time defenders have to respond and how many vulnerabilities can be targeted simultaneously. Security provider Astra therefore does not describe Artex as a new capability for attackers. Instead, it highlights the declining cost per attack attempt, an advantage available to any threat actor, not just those with the expertise to operate the tool.
From Banks to Government Ministries
The European Commission is far from Artex’s first victim. On November 13, the FBI issued a flash alert warning that the tool had been abused since at least August 2026. In some intrusions, attackers obtained privileged access within just three hours.
One of the documented campaigns involved a Chinese threat group that CrowdStrike tracks as Vapor Panda. Starting October 17, a single controller targeted more than 200 organizations in at least 14 countries over an 11-day period. CrowdStrike confirmed post-compromise activity at nine victims, including a Middle Eastern interior ministry and a Latin American foreign ministry. In South Korea, attackers stole customer data from secondary systems operated by Shinhan, KB Kookmin and Hana banks. A seven-member criminal group in Seoul reportedly targeted more than 90 South Korean organizations, successfully breached approximately 60 of them and stole an estimated 8.2 million records.
Original Project Closed, Forks Remain Public
On October 8, the developer switched the project to closed source and stopped releasing updates because the tool was being abused. This did little to curb its availability. Copies, English- and Korean-language derivatives, and forks remain publicly accessible, including ScopeWeaver and ARTEX PRO, a paid version. The number of Artex instances accessible online is also significant. On October 6, AhnLab counted approximately 600 instances. A researcher later identified more than 3,600. The FBI reported more than 1,600 publicly accessible consoles in early November.
There is no patch for Artex itself because the tool exploits existing vulnerabilities. Defenders must therefore focus on hardening their systems and detecting attacks. Recommended measures include phishing-resistant multi-factor authentication and disabling outdated authentication methods. Management interfaces should also be removed from the public internet.
Third Major Security Incident This Year
This is already the European Commission’s third major security incident in 2026. At the end of January, CERT-EU discovered an intrusion into the infrastructure used to centrally manage the Commission’s mobile devices. A considerably more serious incident followed in March. According to CERT-EU, attackers exfiltrated approximately 92 GB of compressed data from an AWS account belonging to the Commission. They had gained access through the compromised Trivy security scanner. This means the Commission has now been targeted twice in 2026 through tools that are actually intended to support cybersecurity defenses.
(Editorial Team)