Thought Leadership
The ransomware group Everest claims to have exfiltrated data belonging to 2,862 employees, training materials for pilots, and Boeing source code. Proof has not yet been provided.
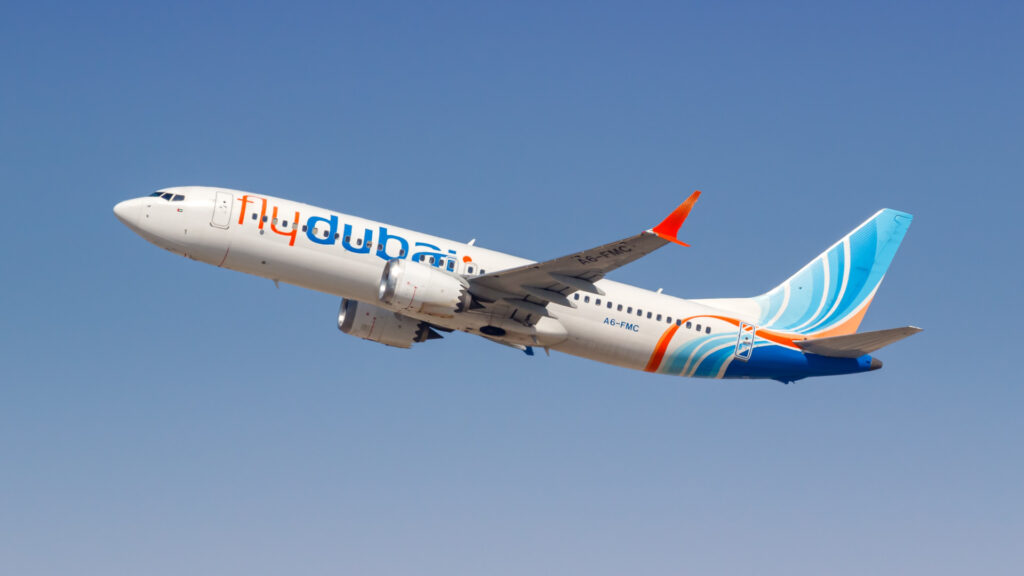
The ransomware group Everest has listed United Arab Emirates airline FlyDubai on its darknet leak site. According to its own statements, it exfiltrated around 4.36 GB of data. The group has not yet published data samples, providing only a detailed list of the allegedly stolen contents. It set a deadline of six days for negotiations. FlyDubai has not yet commented on the claims.
Data of Pilots and Cabin Crew
According to Everest, the dataset comprises 17,053 records on 2,862 employees from the years 2009 to 2020. Affected individuals reportedly include pilots, cabin crew, training managers, flight dispatchers, and ground staff. The data reportedly includes names, employee numbers, job titles, start and end dates of employment, as well as completion dates of training courses and qualification exams.
“With such information, attackers could attempt to target FlyDubai employees via phishing, which could lead to a data breach that also affects other data, including customer data.”
Cybernews
Training Materials and Boeing Software
In addition, Everest claims to have exfiltrated extensive training materials, including a complete interactive course for the Boeing 737NG as well as presentations on topics such as long-range flights over water (ETOPS), de-icing, fog landings, and performance calculations. These reportedly also include operational instructions, such as for landings on icy runways and altimeter settings.
According to the group, the dataset also includes a complete installation package of the Boeing Performance Engineers Tool (PET 3.2). Among other functions, the software calculates takeoff weights, landing distances, and engine failure scenarios. This reportedly includes 2,827 Java source code files, of which well over 2,000 are marked as confidential Boeing proprietary property. Furthermore, Everest claims to have exfiltrated a confidential 190-page CFM engine manual and an Airbus ETOPS guide. Boeing has not commented on the matter.
Group Active Since 2020
Everest has been active since at least 2020 and is attributed to Russia. The group operates under the Ransomware-as-a-Service model and also sells network access to other criminals. In 2025, it claimed an attack on a Coca-Cola bottler in the Middle East and later published its data. Additionally, it claimed responsibility for an attack on Collins Aerospace, whose check-in software failed at several European airports in 2025. This year, Everest listed US financial institutions Frost Bank and Citizens Bank as victims.
(Editorial Team)