Thought Leadership
Japanese company Ikotas executed code on a Galaxy S26 at Pwn2Own Ireland. The Pixel 10 is also reportedly affected.
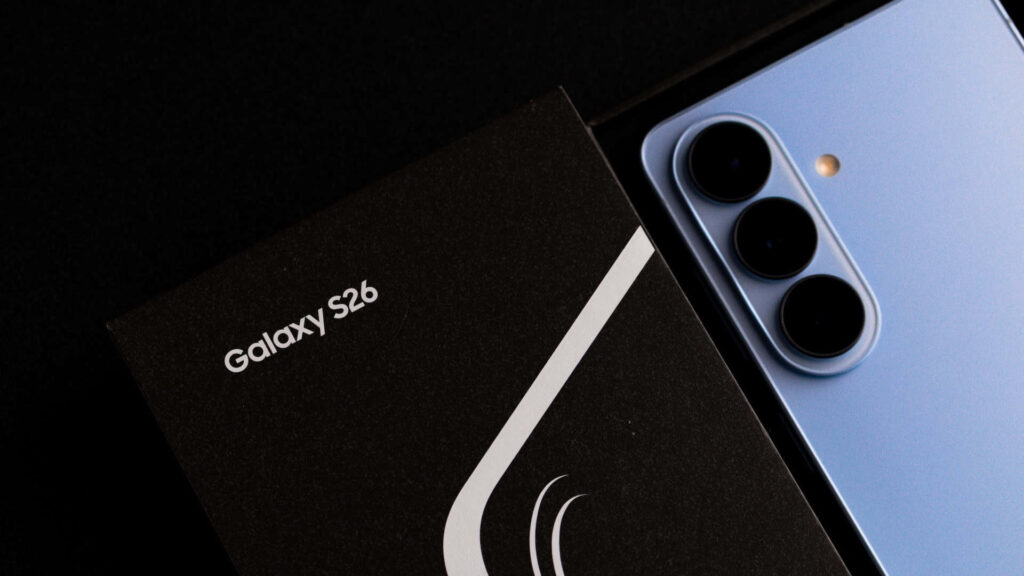
Security researchers from Japanese company Ikotas Labs remotely took control of a Samsung Galaxy S26 at the Pwn2Own Ireland 2026 hacking competition. According to the researchers, a single email sent to the device was enough to carry out the attack. The competition is organized by Trend Micro’s Zero Day Initiative (ZDI).
Ikotas chained together four vulnerabilities for the attack, one of which was already known to Samsung. The company received an $11,000 USD reward for the exploit chain. Overall, three successful attacks against the Galaxy S26 were demonstrated at the competition, involving five apparently new vulnerabilities. Nguyen Thanh Dat of Viettel Cyber Security used four flaws, three of which were already known to Samsung. Interrupt Labs used a chain of four vulnerabilities, including three that had already been discovered by other researchers and one zero-day flaw.
Pixel 10 Also Targeted
On October 1, Ikotas CEO Satoki Tsuji had already announced that the vulnerability also affects Google’s smartphones.
“It’s a zero-day that allows RCE [remote code execution] on the latest versions of Google Pixel 10 (probably works on 11 too) and Samsung Galaxy S26 with just sending 1 email.”
Satoki Tsuji, Ikotas CEO
The researchers also said there is a chain that can subsequently be used to escalate privileges on the device. Tsuji said he had found multiple methods for remotely executing code on each device and planned to report all of them to the manufacturers. According to the ZDI schedule, Ikotas is set to attempt an attack against the Pixel 10 on October 8.
In another post, Ikotas pointed to growing demand for remote smartphone analysis techniques in criminal investigations. The company said it wanted to demonstrate that a Japanese company has the technical capabilities to perform such analysis.
No Technical Details Yet
The ZDI has so far published neither CVE identifiers nor information about the affected components or technical details of the newly demonstrated vulnerabilities. Their severity has therefore not yet been determined. Samsung and Google have not commented on the findings so far.
(Editorial Team)